Most companies’ laptops move across cities, states and even international borders as employees join, change their jobs and depart from the company. The post-laptop return aspect can be forgotten, but it’s one of the most critical pieces of IT asset management.
A retrieved laptop is not handed over to the next employee. It passes through a well-managed process with shipping, tracking, data removal, inspection, refurbishment, inventory update and provisioning. Each step helps to secure company information, to increase the life span of hardware and to avoid unnecessary technology investments.
This article traces the whole life cycle of a company laptop, from an employee’s home workstation to its eventual reassignment to a new user.
What Happens to a Company Laptop After an Employee Leaves?
When an employee leaves, the company laptop does not always follow the same path. After that, it will be up to the condition of the laptop, the needs of the company, and whether or not the laptop is successfully recovered.
In some instances, the laptop will be passed to another employee. If the device requires repairs, it could be repaired or refurbished and then ready for the next use. The working device can also be stored for later use in the field, as can obsolete or unfit machines.
These are the major trails:
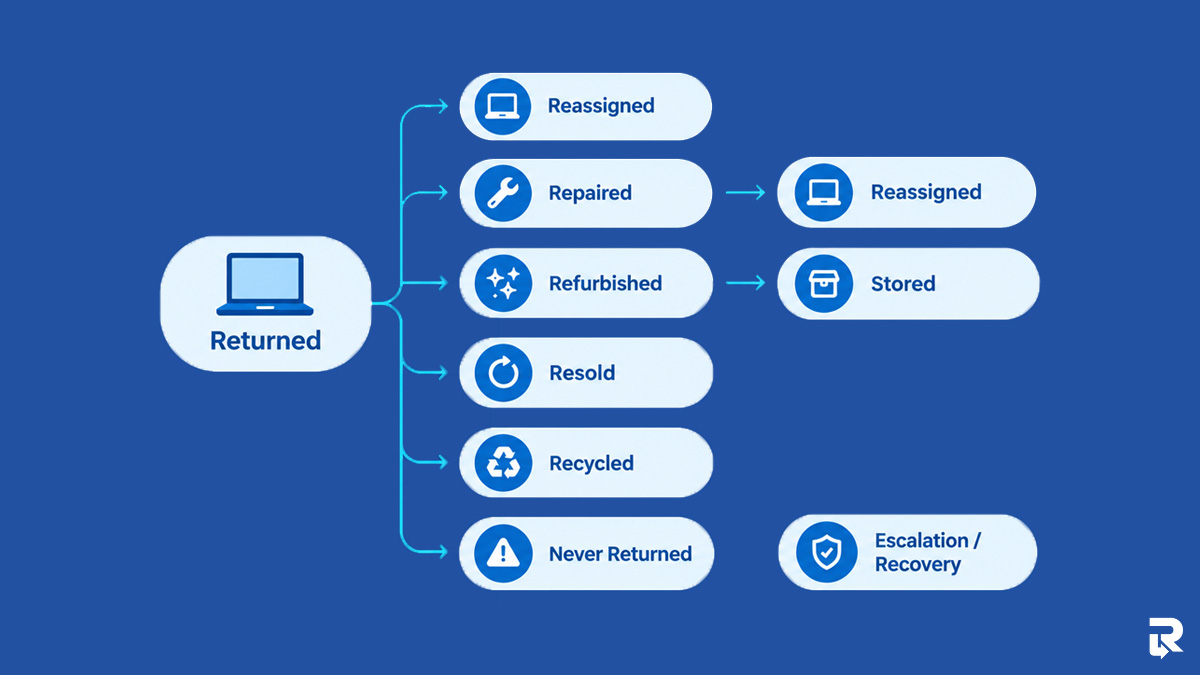
Returned and reused: The laptop is ready for another employee and is prepared in a suitable fashion for that employee before it is returned.
Returned and repaired: Repaired means that the device requires repair and will not be given back.
Returned and held for later: A laptop that is usable can be put back in inventory for later use.
Returned and removed from active use: Depending on its age, condition, or business value, the IT equipment may be resold or recycled.
Not returned: If the employee does not send the laptop back, the case moves into follow-up, escalation, and recovery.
Laptop redeployment is just one of the options, in other words. For the IT team, the key is to know where each device is and ensure its status is continually communicated. This provides the company with a better understanding of what their equipment is, such as whether it is being used by another employee, in storage, leaving the company, or still to be retrieved.
Checklist: What Happens to the Data on a Retrieved Laptop?
The concept of data security should not be limited to post-IT use of the laptop, but should be a factor in the laptop’s journey.
Before Shipping
Prior to the laptop leaving the employee’s hands, IT teams should check if access and device control are in place.
- Disable the employee’s access to company systems
- Revoke active credentials and sessions
- Lock the device when required
- Confirm that the device is encrypted
- Review its MDM/UEM status
- Initiate a remote wipe when appropriate
During Transportation
The device needs to remain visible to the laptop and its movement while it is being transported.
- Employ appropriate and secure containerization
- Follow the whole shipment – from pick-up to delivery
- Record the person who has possession of the device.
- Record major transference of documents during the return.
- Verify delivery to ensure it arrives where it is supposed to be.
After Receipt
After the laptop is received, the IT department will confirm that the device is secure and start the formal data wipe and sanitization procedure.
- Verify the asset tag, serial number, and device identity
- Isolate the device when appropriate
- Sanitize the storage drive using the company’s approved process
- Verify that sanitization was completed successfully
- Record the sanitization result and relevant documentation
Why Companies Retrieve and Reassign Employee Laptops
Replacing every laptop when an employee leaves would be expensive and wasteful. Most of the business devices are still usable for many years, and laptop retrieval and redeployment is a viable solution for organisations of any size.
A structured laptop recovery process can assist companies:
- Reduce hardware purchase expenses through the extension of device life.
- Recover laptops for employees who work remotely rather than buying a new laptop for every new employee.
- Keep sensitive business information secure from unauthorized users.
- Keep inventory and ownership records of assets accurate.
- Help to promote sustainability by minimizing electronics waste.
- Meet internal policies and external compliance requirements.
- Enhance onboarding – stock deployment ready devices.
The security aspect is especially important. An unreturned laptop may contain company emails, documents, customer records, or credentials. According to IBM’s Cost of a Data Breach Report, the global average cost of a data breach reached $4.44 million in 2025. While a missing laptop does not automatically constitute a breach, organizations cannot ignore the risks posed by unreturned laptops, particularly when they contain sensitive data or stored credentials.
Here’s what the journey of a retrieved laptop looks like:
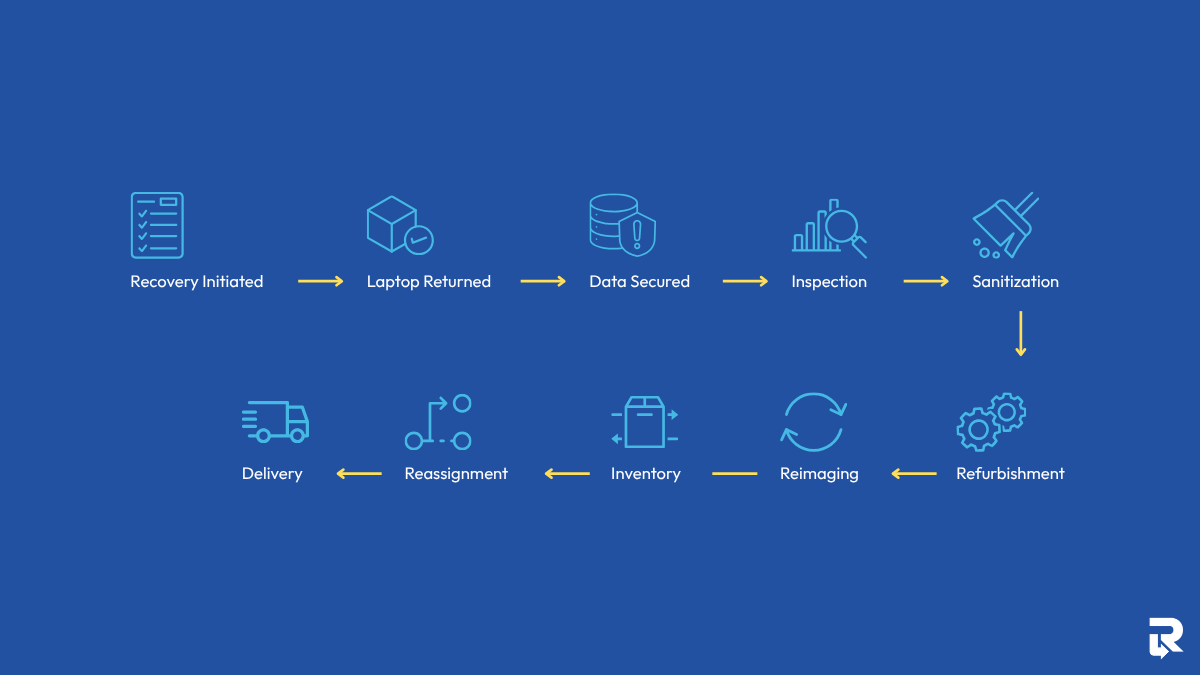
Step 1: Triggering the Laptop Recovery Process
The journey begins as soon as an employee’s departure is confirmed. Whether the exit is planned or unexpected, organizations need a process that ensures company-owned equipment is identified and scheduled for return before important details are forgotten.
HR Initiates the Offboarding Workflow
In many organizations, HR starts the offboarding process by updating the employee’s status in the HR platform. This action typically triggers notifications to IT, security, and asset management teams.
At this stage, teams review:
- Assigned laptop details
- Asset tag and serial numbers
- Employee location
- Return deadlines
- Any accessories issued alongside the laptop
Having a documented process is especially important for companies that need to recover laptops from remote employees spread across different cities or regions.
Creating a Recovery Plan
Before contacting the employee, IT confirms what equipment should be returned.
This often includes:
- Laptop
- Charger
- Docking station
- External monitor
- Security keys or authentication tokens
- Company-issued mobile devices
The goal is to create a complete record before recovery begins.
Why Acting Quickly Matters
The longer a device remains outside company control, the more difficult it can become to retrieve. Employees may relocate, shipping information may change, or equipment may become damaged while sitting unused.
A prompt laptop return process reduces these risks and keeps asset records accurate.
Step 2: Returning the Laptop From the Employee’s Home
Once the recovery request is created, the next step is getting the laptop back safely.
Most organizations try to make the process as simple as possible. If returning equipment becomes complicated, delays become more likely.
Preparing the Return Shipment
Many companies send employees:
- A prepaid shipping label
- Protective packaging materials
- Printed return instructions
- Courier drop-off information
Providing everything upfront removes guesswork and encourages faster returns.
Maintaining Shipment Security
A laptop often contains sensitive company information, making shipping security just as important as convenience. Establishing secure device returns helps organizations reduce the risk of loss, theft, or unauthorized access while equipment is in transit.
To reduce risk, organizations typically:
- Use tracked shipping services
- Require delivery confirmation
- Document custody transfers
- Record shipment milestones
- Monitor return status until arrival
Domestic vs. International Laptop Retrieval Challenges
Recovery becomes more complex when employees work outside the company’s primary operating region. Laptop retrieval challenges also exist; for instance, domestic returns are usually straightforward, but international recoveries may involve:
| Challenge | Potential Impact |
| Customs clearance | Delayed deliveries |
| Import/export regulations | Additional paperwork |
| Regional courier limitations | Limited tracking visibility |
| Taxes and duties | Higher recovery costs |
| Extended transit times | Longer asset recovery cycles |
For global organizations, these factors often influence how recovery programs are designed.
Step 3: Securing Company Data Before the Device Arrives
Even while a laptop is being shipped back, the organization must continue protecting the information stored on it.
This stage focuses on minimizing the cybersecurity risks of unreturned laptops and ensuring company data remains secure throughout transit.
Revoking Employee Access
One of the first actions taken after offboarding is disabling access to corporate resources.
This commonly includes:
- Company email
- VPN connections
- Cloud storage platforms
- Remote work collaboration tools
- Internal business applications
Removing access prevents former employees from connecting to sensitive systems after their departure.
The Two Sides of Laptop Recovery
Laptop recovery is usually considered a physical process: first get the device from the employee to its place, ship it back to the organization, and record its arrival. However, there is another side of the coin we almost ignore or forget. While a laptop is moving through the return process, the company is continuously managing its accounts, access, security controls, and device status.
These two sides are not the same but yes, they are connected. A laptop can be physically on its way back while its former user’s access has already been removed. Likewise, a device can arrive safely at an IT facility while it still needs to go through security and IT managers checks before it can be used again.
Managing the Physical Journey
The physical side focuses on keeping the machine under the control of the employee to the next point it is transported to. It starts with notifying the employee and arranging the return. From there, it is the responsibility of IT or the recovery team to handle packaging and shipping, tracking, receiving, and inspection.
The goal is to ensure where the device is currently, who the owner is, and what condition it is in at each relevant stage. This becomes very crucial when the employees are not in the same place, but are in various locations and the device or equipment has to move throughout all these places or maybe travel internationally.
Managing the Digital Journey
The digital journey begins before the laptop is physically returned. The IT department needs to control the device as well as the access associated with it throughout the transition.
This process includes revoking the former employee’s access, locking the device, monitoring and tracking device status, and using remote management features as needed. Once the device is back under company control, its data can be sanitized and its management status can be updated prior to next use.
Therefore these two sides work together. Physical recovery brings the device back under organizational control, while digital ensures the company information is protected during and post physical recovery.
A Simple Model for IT Teams
This approach to recovery is helpful to spot gaps. A company may have a better shipping process but weak on digital control, or strong endpoint management but no clear way to track the physical device.
The following model shows how the two workstreams can run alongside each other:
| Physical Lifecycle | Digital Lifecycle |
| Employee notified | Account access revoked |
| Return packaging arranged | Device locked |
| Laptop shipped | Device monitored |
| Carrier tracking | Remote wipe where appropriate |
| Device received | Data sanitization |
| Physical inspection | MDM/UEM status reviewed or updated |
| Repair, when needed | Device re-enrolled for its next used |
| Storage or inventory | Security configuration applied |
| Redeployment or other disposition | Compliance verification |
Thinking about both sides together helps IT teams treat laptop recovery as an asset and security process, rather than simply a shipping task. The physical device needs to be accounted for, while the digital access and controls surrounding it need to remain managed throughout its transition.
Using Remote Management Tools
Modern endpoint management platforms allow IT teams to manage devices remotely.
Administrators can often:
- Lock devices remotely
- Remove company accounts
- Restrict application access
- Monitor device status
- Initiate remote wipe procedures
Preparing for Unexpected Situations
Not every recovery goes according to plan.
Devices may be:
- Lost in transit
- Damaged during shipping
- Delayed for weeks
- Returned with security concerns
Having remote controls in place provides an additional layer of protection until the laptop reaches its destination.
According to IBM’s Cost of a Data Breach Report, the average global cost of a data breach reached $4.88 million in 2024, highlighting why organizations take endpoint security seriously.
Step 4: Receiving and Inspecting the Returned Laptop
Once the laptop arrives, it enters a controlled intake process.
Before any refurbishment or redeployment can occur, technicians need to verify the condition of the device and confirm that the correct asset has been returned.
Logging the Device Into Inventory
The first step is recording the laptop’s arrival.
Teams typically document:
- Asset tag number
- Serial number
- Device model
- Date received
- Recovery ticket number
- Employee association history
This creates a complete audit trail for future reference. Tracking this information also helps IT teams measure important remote laptop return program KPIs, such as return completion and recovery performance.
Performing a Physical Inspection
Technicians then evaluate the laptop’s condition.
Areas commonly inspected include:
- Display quality
- Battery health
- Keyboard functionality
- Webcam performance
- Ports and connectors
- Chassis condition
Common Inspection Checklist
| Component | What Is Checked |
| Screen | Cracks, dead pixels, discoloration |
| Battery | Capacity, charging performance |
| Keyboard | Missing or unresponsive keys |
| Ports | USB, HDMI, charging ports |
| Webcam | Functionality and image quality |
| Chassis | Cosmetic and structural damage |
Grading the Device
Many organizations classify returned laptops based on condition.
Typical categories include:
- Excellent condition
- Minor wear
- Moderate wear
- Repair required
- End-of-life
This assessment determines whether the device moves forward to refurbishment or retirement.
Step 5: Data Sanitization and Compliance Verification
Once a retrieved laptop reaches the appropriate stage of processing, the data related to the previous user must be securely eliminated from the device before it can progress to the next phase of processing or to a different type of disposition. This process should document what was done, to which device, and the result of the process.
Why Deleting Files Is Not Enough
Although deleting files or doing a simple reset will not delete all information from a storage drive. Data can still be recovered using specialized tools.
For this reason, organizations rely on controlled data sanitization techniques that are specifically created to eliminate the data stored and also make sure that the process is effective.
Performing Certified Data Erasure
Typically, this process begins by verifying the identity of the device, followed by the prescribed data erasure process. The outcome is then checked and recorded, giving the organization proof of the secure data sanitization of the laptop.
The typical process involves:
- Device verification: Confirm the asset tag, serial number, and device details.
- Erasure execution: Apply the approved data sanitization method.
- Validation testing: Confirm that the erasure was completed successfully.
- Reporting: Record the device, process, result, and relevant details.
- Certification: Generate documentation confirming successful sanitization.
Maintaining Chain of Custody
Chain of Custody (CoC) is another layer of accountability, as it tracks the physical device from its recovery to its sanitization.
For instance, the record can contain data about when the laptop was received, who owns it, when the laptop was sanitized, and when it was done. This establishes a traceable link between the physical asset and sanitization records of the data.
Data Sanitization Workflow
| Stage | Purpose |
| Device Verification | Confirms the correct asset is being processed |
| Chain of Custody | Records handling and custody changes |
| Data Erasure | Removes stored information |
| Validation Scan | Confirms the erasure was successful |
| Report Generation | Documents the process and result |
| Certification | Provides evidence of completed sanitization |
Meeting Regulatory Requirements
For many organizations, secure data removal also needs to support internal policies, contractual obligations, industry requirements, or applicable data privacy rules of retired devices or redeployment. Keeping important compliance considerations and clear records helps demonstrate that the device was handled in accordance with the organization’s established process.
After successful erasure, organizations may generate a Certificate of Data Destruction or similar documentation as evidence of the completed process. Together with the Chain of Custody record, these documents provide a clearer audit trail for the recovered device.
Step 6: Refurbishing the Laptop for Continued Use
Once the data has been removed, attention shifts to restoring the laptop to a condition suitable for another employee.
Cleaning and Cosmetic Restoration
Years of daily use can leave visible signs of wear.
Technicians typically:
- Remove old asset labels
- Clean keyboards and screens
- Sanitize external surfaces
- Remove adhesive residue
- Restore the device’s appearance
A clean device helps create a better experience for the next user.
Repairing or Replacing Components
Not every laptop returns in perfect condition.
Common repairs include:
- Battery replacement
- Keyboard replacement
- SSD replacement
- Charger replacement
- Fan maintenance
Extending Device Lifespan
According to research from the United Nations Institute for Training and Research, extending the usable life of electronic devices can significantly reduce electronic waste generation and lower demand for new manufacturing.
Refurbishment helps organizations maximize value from existing hardware while reducing unnecessary purchases.
Step 7: Reimaging and Re-Enrolling the Device
After refurbishment, the laptop receives a completely fresh software environment.
Installing a Clean Operating System
Technicians deploy a standardized operating system image that aligns with company requirements.
This typically includes:
- Latest operating system version
- Security updates
- Driver updates
- Corporate configurations
Re-Enrolling the Device Into Management Platforms
Most organizations use Mobile Device Management (MDM) or Unified Endpoint Management (UEM) platforms.
These systems allow administrators to:
- Enforce security policies
- Deploy software
- Manage updates
- Monitor compliance
Standardizing the User Experience
Before deployment, approved applications are installed or assigned.
Common examples include:
- Productivity suites
- Communication tools
- VPN software
- Endpoint protection software
- Industry-specific applications
The result is a laptop that is fully prepared for reassignment.
Step 8: Returning the Laptop to Active Inventory
After testing and configuration, the laptop moves back into the organization’s inventory pool.
Updating Asset Records
Asset management systems are updated with:
- Current condition
- Repair history
- Warranty information
- Deployment status
- Location details
Accurate records help organizations make informed purchasing and lifecycle decisions.
Assigning a New Asset Status
Many organizations classify redeployment-ready devices using designated inventory categories.
Examples include:
- Ready for deployment
- Reserved
- In testing
- Awaiting repair
Maintaining Inventory Visibility
Keeping inventory data current helps IT teams quickly identify available equipment whenever a hiring need arises.
Step 9: Assigning the Laptop to a New Employee
The laptop is now ready for its next user.
Selecting the Appropriate Device
Not every employee requires the same hardware specifications.
IT teams consider:
- Job responsibilities
- Performance requirements
- Department needs
- Software demands
Matching devices to roles improves productivity and user satisfaction.
Provisioning User Access
Before shipment, administrators assign:
- User profiles
- Software licenses
- Security permissions
- Department-specific applications
This ensures the device is ready for use immediately after delivery.
Conducting Final Quality Checks
Prior to shipment, technicians often perform:
- Login testing
- Connectivity testing
- Security validation
- Application verification
This final review reduces onboarding issues later.
Step 10: Delivering and Provisioning the Device
The final stage completes the laptop’s journey.
Shipping to the New Employee
Once configured, the laptop is securely packaged and shipped to its new owner.
Organizations typically track:
- Shipment status
- Delivery confirmation
- Receipt acknowledgement
First-Day Setup Experience
When the employee receives the laptop, setup is usually straightforward.
Typical onboarding steps include:
- Connect to Wi-Fi.
- Sign in using company credentials.
- Complete multi-factor authentication.
- Allow automated configuration to finish.
Automatic Deployment of Settings and Applications
Modern management platforms can automatically install:
- Business applications
- Security controls
- VPN configurations
- Compliance settings
- Productivity tools
Within a short period, the laptop is fully operational and ready to support the employee’s daily work.
Laptop Retrieval by Scenario
Not every laptop return follows the same process. The steps, urgency, communication, and recovery challenges can change depending on why the device needs to be retrieved and what is happening with the employee.
Common laptop retrieval scenarios include:
- Remote employee resignation
- Involuntary termination
- Employee relocation
- Employee leaves the country
- Lost laptop
- Damaged laptop
- Employee refuses to return equipment
- Employee is unreachable
- Contractor or temporary worker
- M&A or company acquisition
- Mass layoffs
- Office closure
- Large-scale device refresh
- Hybrid workforce
Each situation can require a different recovery approach. For example, a planned resignation may allow time to arrange a standard return, while a lost device or involuntary termination may require faster coordination and additional controls.
These scenarios are worth considering separately because the right recovery process depends on the circumstances surrounding the device. The sections below can explore each scenario in greater detail.
Managed Recovery vs. DIY Laptop Retrieval
Some organizations manage recovery programs internally, while others partner with IT asset recovery specialists.
A DIY laptop retrieval approach may work for smaller businesses with limited device volumes. However, organizations with remote workforces often benefit from specialized providers that can coordinate logistics, maintain chain-of-custody records, perform certified data sanitization, and prepare devices for redeployment at scale.
Conclusion
A company laptop does not end its life when an employee leaves. It simply changes hands. From recovery and shipping to sanitization, repair, and redeployment, each stage plays a role in keeping devices secure and useful for longer.
When this process is structured, organizations reduce risk, avoid unnecessary hardware costs, and keep sensitive data protected at every step. It also ensures new employees receive ready-to-use devices without delays or confusion.
For businesses looking to simplify global asset recovery and ensure consistent handling across locations, Remote Retrieval offers support for safe, trackable, and secure device returns worldwide.
For Enterprise Solutions